Definitions:
-
"Next Release". The next version to be released.
-
"Latest Release". The latest YY.N Version released by Anjana Data and, if any, its latest active Patch.
-
"GA (General Availability)". Date from which a Version is considered released for general use.
-
EOS (End of Support): End of support.
For further detail, see the Anjana Data Support Policy
26.1 Patch 2 - 25/08/2026
26.1 Patch 2
Core
|
1.0.0 |
5.0.0 |
5.2.0 |
6.0.0 |
6.0.1 |
6.1.0 |
|---|---|---|---|---|---|
|
marketplace |
inventory-interceptor |
tot anjana-ui portuno-ui |
hermes
drittesta |
kerno🆕 minerva🆕 |
zeus |
Tot Plugins
|
1.0.0 |
5.0.0 |
5.1.0 |
5.2.0 |
5.2.1 |
|---|---|---|---|---|
|
tot-plugin-databricks tot-plugin-snowflake🆕 |
tot-plugin-aqtiva |
tot-plugin-aws-s3 tot-plugin-azure-ad tot-plugin-azure-storage tot-plugin-gcp-iam tot-plugin-jdbc-snowflake |
tot-plugin-aws-glue tot-plugin-aws-iam tot-plugin-gcp-bigquery tot-plugin-gcp-storage tot-plugin-jdbc tot-plugin-jdbc-oracle tot-plugin-jdbc-redshift tot-plugin-jdbc-sqlserver tot-plugin-ldap tot-plugin-powerbi tot-plugin-tableau |
tot-plugin-jdbc-denodo |
AI
|
1.0.1 |
|---|
|
adp-mcp🆕 |
Installers
|
Ansible |
K8S |
Installer |
|---|---|---|
|
26.a1.1788858836 |
26.k1 |
1.0.1 |
Updates
Minerva
The connection client between the platform indexing module and the search engine has been modernized, migrating to the HTTP/2-based implementation supported by the current versions of Solr. The change aligns the platform with the engine version incorporated in 26.1, removes deprecated connection components and improves search stability during indexing schema update operations.
Kerno
An error has been fixed whereby, when approving the modification of a dataset, the fields referenced in attributes of type ENTITY_CONTAINER, ENTITY_SEARCH or ARRAY_ENTITY stopped appearing in the content. Modified fields now retain their identity after the flow is approved, applying the same behaviour that the parent DATASET already had, so that existing references in the aforementioned attribute types remain valid. The search index update of the affected objects is also completed when fields of the associated dataset are modified or deleted, preventing them from showing outdated information.
The patch includes an automatic repair process for the attributes that may have been affected in existing environments.
Related bug: D13131 https://wiki.anjanadata.com/es/portal-de-soporte/current/problemas-y-limitaciones-conocidos
ADP-MCP
An error in the MCP server login flow has been fixed whereby certain users could not complete authentication and received a generic authentication error message. Error traceability in the logs has also been improved.
In addition, the authorization flow is reinforced with mandatory PKCE (S256), together with other security improvements. It is recommended to deploy this version of the MCP server.
Related bug: DS4920 https://wiki.anjanadata.com/es/portal-de-soporte/current/problemas-y-limitaciones-conocidos
Tot-Plugin-Snowflake
A new integration plugin for Snowflake is released, based on the Snowflake SQL API and OAuth2 authentication with Microsoft Entra ID (External OAuth), which replaces the previous plugin based on a JDBC connector. In addition to metadata extraction and data sampling —now with support for tables, views and materialized views, and retrieval of native Snowflake tags, including those inherited from ancestor assets—, the new plugin extends the functional scope with access permission management: creation and management of roles associated with Data Sharing Agreements and automatic granting and revocation of consumption privileges on the governed assets. Permission management requires the Entra ID plugin deployed and Azure SSO enabled.
With the release of this plugin, the Snowflake plugin via JDBC is deprecated. It will remain available throughout the 26.1 lifecycle, but will not receive new features or updates, so it is recommended to plan the migration to the new plugin as soon as possible.
More information in the plugin documentation: Snowflake (Native API)
Bugs
All the information relating to the problems and limitations that apply to this version or that have been fixed is available in the documentation under Support portal > Known problems and limitations Known Issues and Limitations .
26.1 Patch 1 - 17/08/2026
26.1
Core
|
1.0.0 |
5.0.0 |
5.2.0 |
6.0.0 |
6.1.0 |
|---|---|---|---|---|
|
marketplace |
inventory-interceptor |
tot anjana-ui portuno-ui |
hermes
kerno minerva drittesta |
zeus |
Tot Plugins
|
1.0.0 |
5.0.0 |
5.1.0 |
5.2.0 |
5.2.1 |
|---|---|---|---|---|
|
tot-plugin-databricks |
tot-plugin-aqtiva |
tot-plugin-aws-s3 tot-plugin-azure-ad tot-plugin-azure-storage tot-plugin-gcp-iam tot-plugin-jdbc-snowflake |
tot-plugin-aws-glue tot-plugin-aws-iam tot-plugin-gcp-bigquery tot-plugin-gcp-storage tot-plugin-jdbc tot-plugin-jdbc-oracle tot-plugin-jdbc-redshift tot-plugin-jdbc-sqlserver tot-plugin-ldap tot-plugin-powerbi tot-plugin-tableau |
tot-plugin-jdbc-denodo🆕 |
AI
|
1.0.0 |
|---|
|
adp-mcp |
Installers
|
Ansible |
K8S |
Installer |
|---|---|---|
|
26.a1 |
26.k1 |
26.1 |
Updates
Denodo plugin
Evolution of the plugin's functionality in the permissions granting flow to grant and revoke CONNECT permission on the Virtual Database (GRANT CONNECT, REVOKE CONNECT).
More information in the plugin documentation Denodo
Bugs
All the information relating to the problems and limitations that apply to this version or that have been fixed is available in the documentation under Support portal > Known problems and limitations.
26.1 GA - 29/06/2026
26.1
Core
|
1.0.0 |
5.0.0 |
5.2.0 |
6.0.0 |
6.1.0 |
|---|---|---|---|---|
|
marketplace🆕 |
inventory-interceptor |
tot🆕 anjana-ui🆕 portuno-ui🆕 |
hermes🆕
kerno🆕 minerva🆕 drittesta🆕 |
zeus🆕 |
Tot Plugins
|
1.0.0 |
5.0.0 |
5.1.0 |
5.2.0 |
|---|---|---|---|
|
tot-plugin-databricks🆕 |
tot-plugin-aqtiva |
tot-plugin-aws-s3🆕 tot-plugin-azure-ad🆕 tot-plugin-azure-storage🆕 tot-plugin-gcp-iam🆕 tot-plugin-jdbc-snowflake🆕 |
tot-plugin-aws-glue🆕 tot-plugin-aws-iam🆕 tot-plugin-gcp-bigquery🆕 tot-plugin-gcp-storage🆕 tot-plugin-jdbc🆕 tot-plugin-jdbc-denodo🆕 tot-plugin-jdbc-oracle 🆕 tot-plugin-jdbc-redshift🆕 tot-plugin-jdbc-sqlserver 🆕 tot-plugin-ldap🆕 tot-plugin-powerbi🆕 tot-plugin-tableau🆕 |
AI
|
1.0.0 |
|---|
|
adp-mcp🆕 |
Installers
|
Ansible |
K8S |
Installer |
|---|---|---|
|
26.a1🆕 |
26.k1🆕 |
26.1🆕 |
Required manual actions
Before the upgrade
-
Update the deployment kit to its latest version, if not done yet. Review the specific documentation of the kit versions.
-
If any installation kit provided by Anjana Data is used, in order to have the software fully updated it is only necessary to update the artefact versions with the values mentioned in the previous section Affected artefacts; the software takes care of the database changes. Only otherwise, the persistence versions will have to be updated to their latest production version, manually by the installer.
Before considering the upgrade complete
During the initial startup, Portuno migrates the configuration from the old Administration Portal to the new one (from PostgreSql to documentsDB). Once Portuno appears as UP in Horus, it is necessary to restart the platform from the installer in order to run the liquibase of each microservice that depends on the Portuno configuration.
To verify that the above has been executed successfully:
-
Access the database and verify that the databasechangelog tables of the anjana, hermes, minerva, portuno and zeus schemas contain records corresponding to the 26.1 liquibase. To do so, filter the filename column by
filename like ('%/26.1/%') -
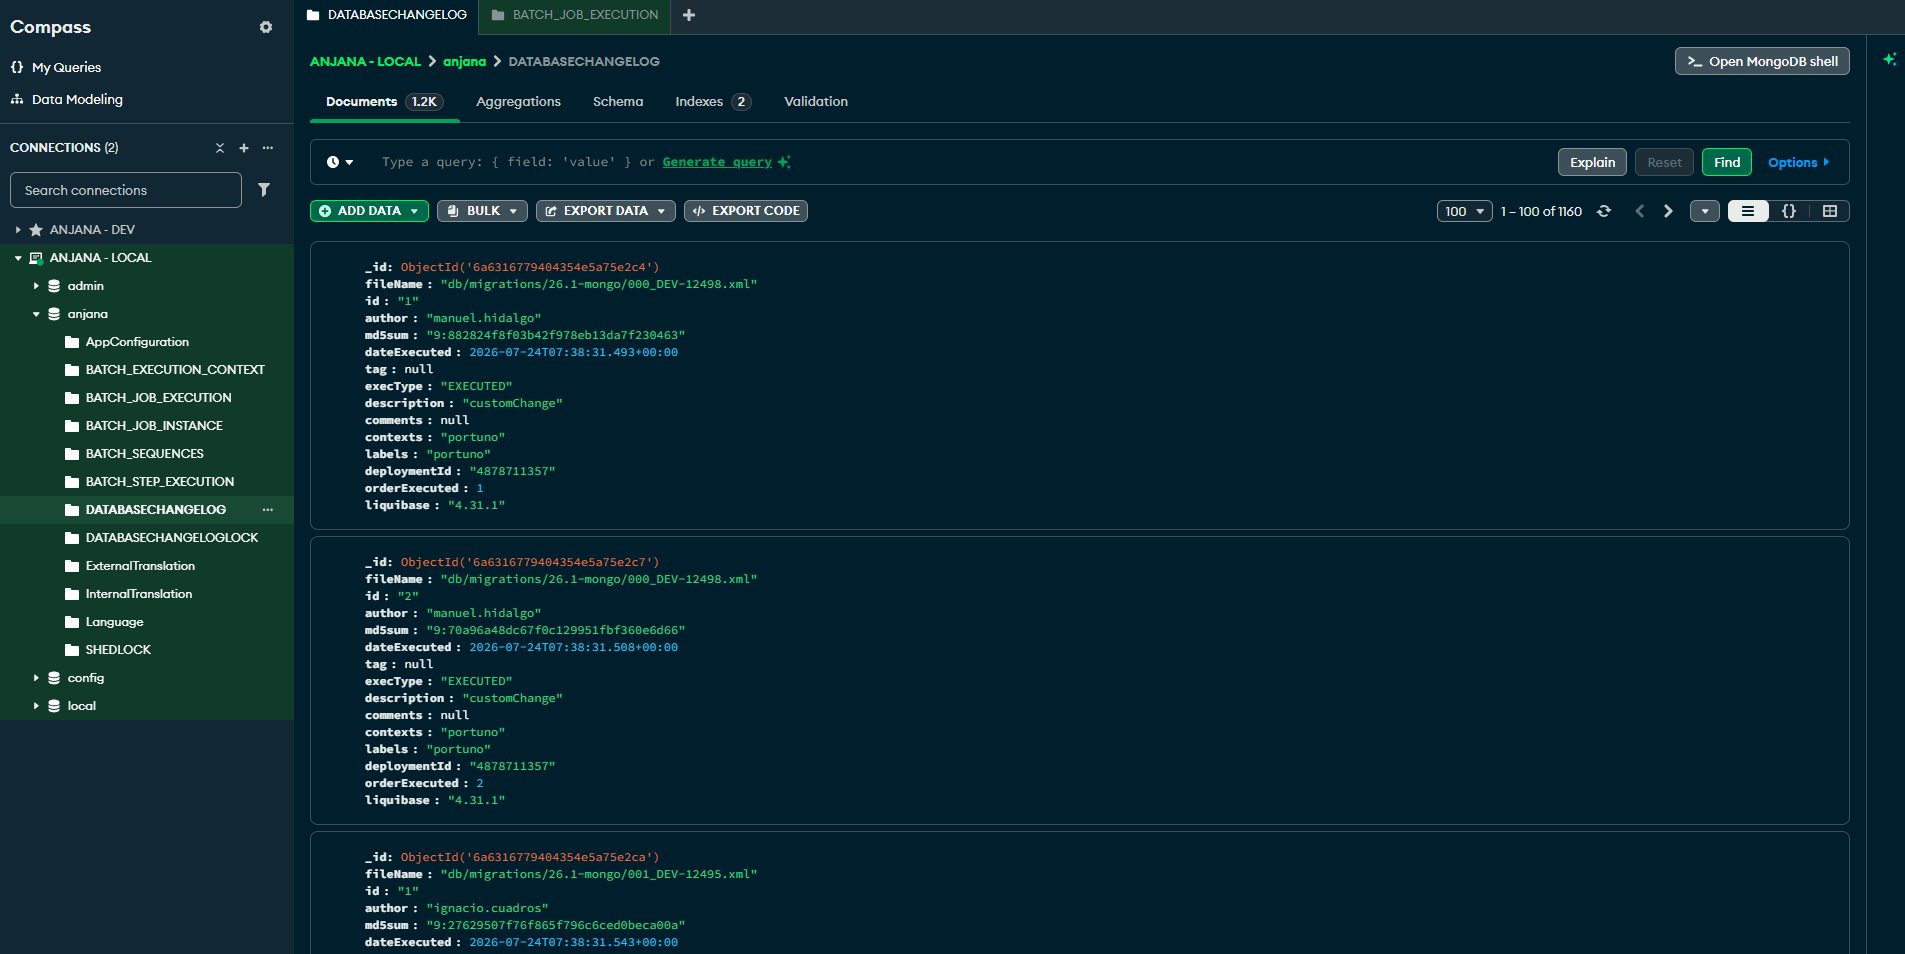
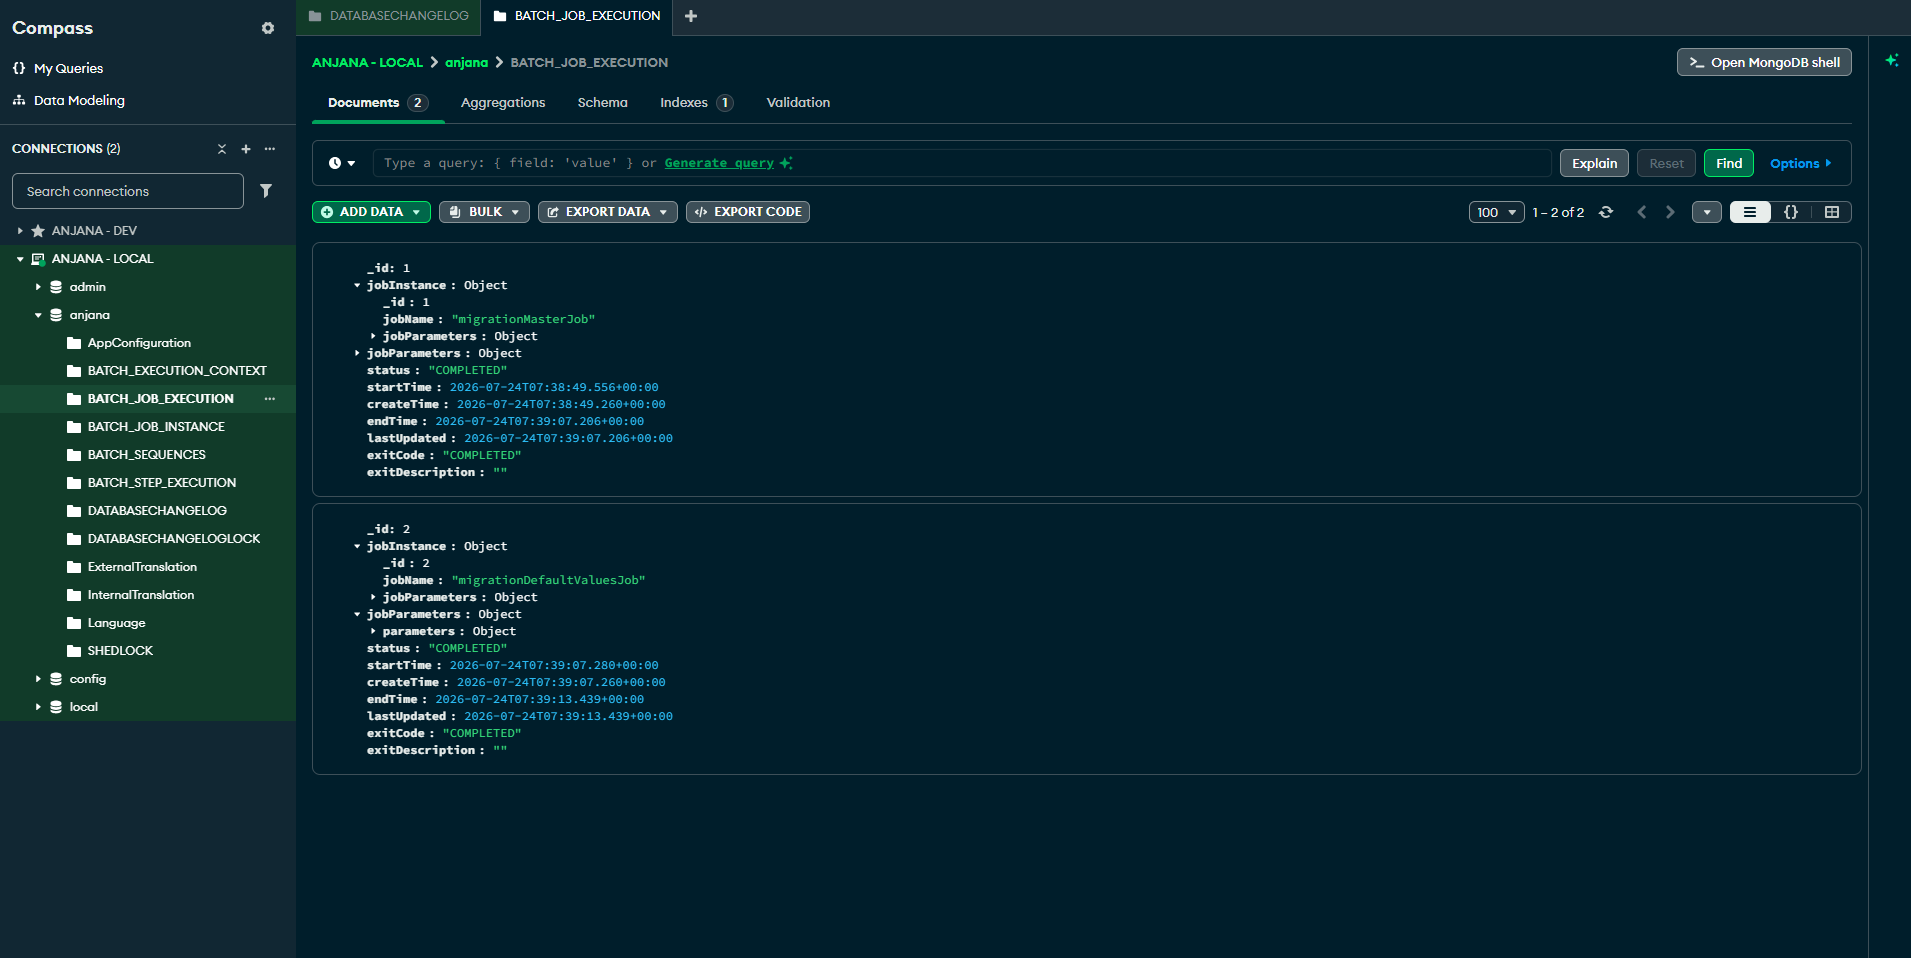
Access documentsDB and verify:
-
The DATASABECHANGELOG table is available with the records of
db/migrations/26.1/
-
The BATCH_JOB_EXECUTION table is available and contains 2 records, one corresponding to the migrations of the i18n translation records and appConfigurations, and another one for the insertion of the default translations, both in status COMPLETED
-
Optional manual actions
-
If weightings were set in SolR, they will probably have to be regenerated given the volatile nature of the indexer
-
It is recommended to include the #REQUEST_REASON# variable in the body of the notifications associated with workflow alerts, so that the participants receive the texts associated with the request reason that is incorporated for all workflows in this version.
-
If notifications have been configured with an external provider (for example, via email), it is advisable to review the Notifications configuration in the Administration Panel in order to keep receiving them. By default, the migration leaves the EXTERNAL_SENDING field empty, so notifications will not be received.
-
From the new administration portal:
-
Reindex everything.
-
-
Review the Authentication mechanisms implemented and assess the migration of those that have been deprecated in this version before their expiry in 26.2.
Updates
Update in the deployment kits:
Ansible
Blocking changes
-
New deployment role for MongoDB 7.0
-
New deployment role for RabbitMQ 3.12
-
New deployment role for Valkey 7.2 and connection strings for new persistences: MONGO_URI, VALKEY_*, RABBITMQ_*
-
New deployment role for the marketplace microservice (port 8089), includes the creation of its schema in PostgreSQL during the update
Other changes and optimizations
-
Eureka and Spring Boot Admin URLs configured through environment variables (HORUS_REPLICAS, HORUS_ADMIN_URL, TOT_EUREKA_URL) in the systemd units, instead of Spring arguments
-
Variables in hosts.yaml for single-node and multi-node deployments
-
TLS certificate backup included in the Ansible backup
-
Correction of names in service templates
-
Correction of S3 properties
-
HTTP security headers added to the Apache VirtualHost, removal of the obsolete Swagger proxy and replacement of the MD5 trace ID with
Apache UNIQUE_ID -
Grafana exposed through the Apache proxy at
/grafana(port 443) -
JVM memory model aligned:
MaxRAMPercentage+systemd MemoryMaxinstead ofXmx(fixed) -
Solr:
SOLR_HEAPreplaced bySOLR_JAVA_MEM, withGC_TUNEset explicitly -
systemd dependencies (
After=/Wants=) between core services and plugins for an ordered startup -
Compatibility with RHEL 9 and Ubuntu 24.04 (Python 3.12, pymongo 4+, Remi repository, PPA) for the new MongoDB, Valkey and RabbitMQ persistences
-
Idempotency improvements in the installation roles (Solr, artefact copy, SHA1 check of downloads) to allow safe re-runs of the playbook
-
New
delete-solrzkanddelete-miniotags for selective uninstallation -
New warnings in
anjana.shindicating the mandatory steps to deploy MongoDB, RabbitMQ and Valkey before updating the microservices
K8s Kit
Blocking changes
-
Complete restructuring of the kit: from flat YAML manifests (122 files) to a Helm chart with anjana-core and anjana-plugins subcharts (11 reusable templates). Deployment via helm install/upgrade
-
TLS automated with cert-manager: internal mode (auto-generated self-signed certificates + truststore generation Job) and manual mode (pre-created secrets)
-
IRSA support for Horus: integration with AWS Secrets Manager as config server backend, with validation guard rails
-
Multiple config server backends: AWS Secrets Manager, Git or pure JDBC mode (Horus own credentials via Kubernetes Secret), selectable via values.yaml
-
Standalone mode for plugins: direct reading of cloud secrets (AWS SM, Azure KV, GCP SM) without the need for a config server
-
Optional manifests for new persistences: MongoDB, RabbitMQ, Valkey
-
Migration from MinIO to SeaweedFS as S3/CDN storage backend: new seaweedfs.yaml manifest replaces minio.yaml
-
InitContainers to wait for dependencies: ordered service startup with HTTPS health checks between them
Other changes and optimizations
-
Eureka and Spring Boot Admin URLs configured through environment variables (HORUS_REPLICAS, HORUS_ADMIN_URL, TOT_EUREKA_URL) instead of Spring arguments
-
Native OpenTelemetry integration: OTEL_SERVICE_NAME and OTEL_RESOURCE_ATTRIBUTES injected into all services
-
AES backend scripts
-
extraCaBundles support in the truststore Job to inject additional CAs (e.g. corporate CA)
-
Resource profiles per environment (DEV/PRE/PRO) with automatic selection via global.environment.profile
-
HTTP security headers in the nginx ConfigMaps, login rate limiting on /gateway/public/, X-traceId forwarding to the backends and to portuno-ui, CORS restriction in viator via global.domain, and removal of the obsolete Swagger proxy
-
Loading page for anjana-ui with the health status of the services (HEALTH_LOCATIONS_CONF / HEALTH_MANIFEST_JSON)
-
Solr: default storage changed from emptyDir to hostPath
-
Auto-generated documentation with helm-docs, integrated into a Makefile target
-
Multiple chart validation and runtime behaviour corrections following E2E tests on EKS (database schemas, keystore/truststore in manual mode, resources, health checks)
Update on the platform:
Anjana Data Platform MCP
Version 26.1 incorporates the Anjana Data Platform MCP (Model Context Protocol), which exposes the platform capabilities through the MCP protocol for integration with AI assistants and agents. It is available for both SaaS and IaaS/PaaS deployments.
The Anjana Data Platform MCP is released as a new feature that may contain errors. Before using it, please note that:
-
It is a new and still barely tested feature, which may present failures or unexpected behaviours.
-
It is offered «as is», with no guarantees of stability or completeness, and its use in critical production processes is not recommended.
-
It is not covered by the Anjana Data Support Policy: the commitments regarding incident resolution, delivery of fixes and response times described in that policy do not apply to it.
-
We welcome feedback from those who use it: your comments will help us stabilize and evolve the feature in upcoming versions.
-
Availability: SaaS and IaaS/PaaS deployments.
Extension of the Power BI plugin capabilities
The Power BI Tot Plugin incorporates access management over the Power BI assets catalogued in Anjana Data Platform. The feature allows effective permissions in Power BI to be granted and revoked based on the lifecycle of a DSA, using Azure Entra ID groups as the only authorization unit.
New plugin for metadata extraction over Databricks
In its Phase 1, the integration enables the discovery and extraction of technical metadata (read-only mode) of the assets available in Unity Catalog, without performing any mutation on the source system.
Expand and set application permissions
From this version onwards, access to all modules and access to the tabs of the object view depend on permissions associated with the user's role. This makes the permission configuration more complex but provides greater access granularity, simplifying access to information by user groups.
To this end, the following viewing permissions will be added:
-
Access to the Catalogue module: CATALOG_ACCESS
-
Access to the Jobs module: JOBS_ACCESS
-
Access to full security Audit: SEC_AUDIT_ACCESS
Permission created but without functional capability until release 26.2, planned for Q3 2026
-
Access to full governance Audit: GOV_AUDIT_ACCESS
-
Access to the personal Workspace: WORKSPACE_ACCESS
-
Access to the Relationships tab of an entity: OBJ_RELATIONS_ACCESS
-
Access to the Stakeholders tab OBJ_STAKEHOLDERS_ACCESS
-
Access to the object Audit tab (OBJ_AUDIT_ACCESS)
-
Access to the Versions tab: OBJ_VERSIONS_ACCESS
-
Access to the Data sample tab OBJ_SAMPLE_DATA_ACCESS
-
Access to the Adherence information in the stakeholders tab ADHERENCE_VIEW
A new permission is also included to edit the Access information received by adhered users: EDIT_ACCESS_INFO (action) ALL (subType)
Changes in existing permissions:
-
The ACCESS ALL permission to access the data portal is replaced by the PLATFORM_ACCESS (action) permission with subType ANJANA.
-
The ADMIN (action) ANJANA (subType) permission for the configuration/administration panel is replaced by ADMIN_ACCESS (action) ANJANA (subType)
-
The WIZARD (action) ALL (subType) permission is removed. The creation wizard will be accessed through the creation permissions (CREATION_MODIF) over any subType.
-
The ACCESS (action) ADHERENCE (subType) permission to grant access to data is updated to ADHERENCE_ACCESS (action) ALL (subType). This permission also grants access to the new Marketplace module.
Workflow evolutions
Add request reason for any workflow
All workflows will be completed with the request reason, just as previous versions did with adherence workflows.
To this end, when the user chooses or confirms an action that triggers a workflow, Anjana Data Platform will show a window where the user can enter the reason in at least one of the application languages.
The texts can be consulted from the workflow screens and in the notifications by using the #REQUEST_REASON# variable. It is suggested to include this variable in the body of the workflow notifications, thus ensuring that the users involved receive it.
New workflow screens
From now on, the following screens will be available:
-
My access requests 🆕 : Provides access to adherence workflows requested by the user themselves
Access restriction: Only available for users who either have ADHERENCE permissions, or have been Requesters in an ADHERENCE workflow. -
My governance requests 🆕 : Provides access to governance workflows requested by the user themselves, except for adherence workflows.
Access restriction: Only available for users who either have CREATION_MODIF, CHANGE_OU, CHANGE_OU or DEPRECATION permissions, or are users who have been Requesters in a CREATION, MODIFICATION, ACTIVATION, DEACTIVATION, RENAMING or TRANSFER workflow. -
My Tasks 🆕 : Provides access to workflows that the user has to validate due to their role.
Access restriction: Only available for users who are Validators in a workflow. -
Workflows: Provides access to the complete set of workflows.
Access restriction: Only available for users whose role has WORKFLOW_ACCESS permissions
When a user receives a validation notification, they will always be able to access the workflow to approve or reject it from the notification, from the My Tasks screen or from the complete list of Workflows (only if they have the WORKFLOW_ACCESS permission).
More information on the workflow screens
The information displayed on the workflow screens has been enriched, so from now on it includes:
-
Object
-
Request type
-
Requester
-
Reason
-
Request date
-
Validation status
-
Last participant
-
Last response
-
Time without response
-
Total duration
Some attributes may be omitted on certain workflow screens due to their redundancy. For example, on the "My governance requests" screen the "Requester" is not shown, since that field always corresponds to the user accessing it.
User interface evolutions
Home page
A home page is included as the entry point for users after logging in, and it will be accessible from the Anjana Data Platform and customer logos in the header.
This home page includes:
-
A search engine that allows searches in the Catalogue or in the Marketplace
-
Activity summary with a date range selector (7 days, 30 days, 3 months, 6 months and 1 year)
-
My access requests
-
My governance requests
-
My tasks
-
-
Quick access to:
-
Creation wizard
-
Personal workspace
-
-
Date of the previous login.
Marketplace Portal
A new module called Marketplace is created, intended to be a portal for consumers to search for and request access to assets available for consumption through Data Sharing Agreements (DSA).
The Marketplace first offers a suggestions space where the consumer can view recently added DSAs and the assets most requested by other users.
It then offers a space for asset discovery through a search engine and filters, with an intuitive and agile experience supported by the following capabilities:
-
Save highlighted searches with the option to select one as a favourite.
-
Option to request immediate access or add to the cart for bulk requests
-
Bulk selections of objects to add to the cart
-
Bulk selections to add to the personal workspace
-
Preview the details of an object
-
Consult access information
Platform contract and terms of use
When logging in for the first time in this version, the user will be shown a terms of use contract for the platform which must be accepted in order to continue using it.
Access Information on objects
Users who are adhered to an object will be able to access its access information, where instructions can be included on how to access the physical asset that the object represents.
Only those with EDIT_ACCESS_INFO can modify the access information.
Update in the API:
SUMMARY: 43 added · 43 removed · 22 DEPRECATED
KERNO
✨ New Endpoints (5)
PUT /api/admin/kerno/clear-all (AdminAPIController)
POST /api/common/v1/massiveSubmit/{objectSubType} (CommonController)
POST /api/entity/v1/rename/{objectSubType}/{idObject} (EntityController)
POST /api/relationship/v1/rename/{objectSubType}/{idObject} (RelationshipController)
POST /api/dataset/v1/structure/{idDataset} (DatasetController)
❌ Removed Endpoints (33)
PUT /api/admin/kerno/name/{objectType} (AdminAPIController)
POST /api/v2/attribute/custom/list (AttributeController)
GET /api/v2/common/stakeholders/{objectType}/{objectSubType}/{idObject} (CommonV2Controller)
POST /api/v2/common/massiveSubmit/{objectSubType} (CommonV2Controller)
POST /api/v1/metadata/requests (MetadataController)
POST /api/v1/metadata/requests/detail (MetadataController)
GET /api/v1/dataset/versions/{idObject} (DatasetController)
GET /api/v1/dsa/versions/{idObject} (DsaController)
GET /api/v1/dsa/datasets/{idObject} (DsaController)
POST /api/v1/dsa/datasets/{idObject} (DsaController)
GET /api/v1/instance/versions/{idObject} (InstanceController)
GET /api/v1/instance/project/{idObject} (InstanceController)
GET /api/v1/instance/solutions/{idProcessInstance} (InstanceController)
GET /api/v1/process/versions/{idObject} (ProcessController)
GET /api/v1/process/instances/{idProcess} (ProcessController)
GET /api/v1/solution/versions/{idObject} (SolutionController)
GET /api/v1/solution/instances/owned/{idObject} (SolutionController)
GET /api/v1/solution/instances/related/{idObject} (SolutionController)
POST /api/v1/solution/instances/related/{idObject} (SolutionController)
POST /api/v2/entity/create/{objectSubType} (EntityControllerV2)
GET /api/v2/entity/relationships/{objectSubType}/{idEntity} (EntityControllerV2)
GET /api/v2/entity/complete-dynamic-catalog/{objectSubType} (DynamicCatalogControllerV2)
GET /api/v2/entity/dynamic-catalog/{objectSubTypeParam}/{idObject} (DynamicCatalogControllerV2)
GET /api/v2/entity/dynamic-catalog/{objectSubType} (DynamicCatalogControllerV2)
GET /api/v2/relationship/dynamic-catalog/{objectSubType} (DynamicCatalogControllerV2)
GET /api/v2/relationship/dynamic-catalog/{objectSubType}/{idObject} (DynamicCatalogControllerV2)
GET /api/v2/excel/{objectType}/{objectSubType} (ExcelController)
GET /api/v2/objectsubtypes/{objectType} (ObjectSubtypeController)
GET /api/v2/objecttypes/objectsubtypes (ObjectsAnjanaController)
GET /api/v2/objecttypes/{objectType} (ObjectsAnjanaController)
GET /api/v2/graphics/getAll (GraphicsController)
GET /api/v2/graphics/listGraphics/{objectType}/{idObject} (GraphicsController)
GET /api/v2/graphics/myLineage (GraphicsController)
⏲️ Deprecated Endpoints (4)
POST /api/v5/common/massiveSubmit/{objectSubType} (CommonControllerV5)
POST /api/v5/entity/rename/{objectSubType}/{idObject} (EntityControllerV5)
POST /api/v5/relationship/rename/{objectSubType}/{idObject} (RelationshipControllerV5)
POST /api/v4/dataset/structure/{idDataset} (DatasetControlerV4)
MINERVA
✨ New Endpoints (8)
PUT /api/admin/minerva/clear-all (AdminAPIController)
POST /api/v4/audit/search/AUDIT_OBJECT (AuditController)
GET /api/saved-searches/user/v1/{where} (SavedSearchController)
GET /api/saved-searches/user/v1/{where}/{id} (SavedSearchController)
POST /api/saved-searches/user/v1/{where} (SavedSearchController)
PUT /api/saved-searches/user/v1/{where}/{id} (SavedSearchController)
DELETE /api/saved-searches/user/v1/{where}/{id} (SavedSearchController)
POST /api/indexer/marketplace/v1/search (MarketplaceSearchController)
❌ Removed Endpoints (4)
DELETE /api/admin/minerva/collection/kerno (AdminAPIController)
DELETE /api/admin/minerva/collection/delete-field/{field}/kerno (AdminAPIController)
PUT /api/admin/minerva/collection/update/kerno (AdminAPIController)
POST /api/v4/audit/search (AuditController)
⏲️ Deprecated Endpoints (3)
GET /api/v2/favorite/user (FavoriteSearchController)
POST /api/v2/favorite/user/save (FavoriteSearchController)
POST /api/v2/favorite/user/delete (FavoriteSearchController)
HERMES
✨ New Endpoints (6)
GET /api/workflow/v1/permissions (WorkflowController)
POST /api/workflow/v1/search (WorkflowController)
POST /api/workflow/v1/user/adherence/search (WorkflowController)
POST /api/workflow/v1/user/search (WorkflowController)
POST /api/workflow/v1/user/validation/search (WorkflowController)
PUT /api/admin/hermes/clear-all (AdminAPIController
⏲️ Deprecated Endpoints (2)
POST /api/v2/workflow (WorkflowControllerV2)
GET /api/v1/workflow/execution/{id} (WorkflowOldController)
ZEUS
✨ New Endpoints (7)
PUT /api/admin/zeus/clear-all (AdminAPIController)
GET /public/v6/auth/oidc/login (OidcRestController)
GET /public/v6/auth/saml2/login (SamlRestController)
POST /api/user-language/v1/update (UserLanguageController)
GET /api/user-language/v1/obtain (UserLanguageController)
POST /api/user/v1/autocomplete (UserAutoCompleteController)
POST /api/user/v1/signed (UserSignedController)
❌ Removed Endpoints (5)
GET /api/v2/auth/user (AuthorizationInfoControllerV2)
GET /api/v2/organizationalunit/list/all (OrganizationalUnitControllerV2)
GET /api/v2/organizationalunit/tree/{objectSubtype}/{permission} (OrganizationalUnitControllerV2)
GET /public/v4/auth/licensed (AuthenticationPublicControllerV4)
POST /public/v4/auth/logout (AuthenticationPublicControllerV4)
⏲️ Deprecated Endpoints (11)
POST /api/admin/zeus/create/userLanguage (AdminAPIController)
PATCH /api/admin/zeus/update/userLanguage (AdminAPIController)
DELETE /api/admin/zeus/delete/userLanguage (AdminAPIController)
POST /api/v2/auth/roles/byActionAndOrganizationalUnit (AuthorizationInfoControllerV2)
POST /public/v4/auth/login/oidc/{provider} (AuthenticationPublicControllerV4)
POST /public/v4/auth/login/oidc/password/{provider} (AuthenticationPublicControllerV4)
POST /public/v4/auth/login/password/{provider} (AuthenticationPublicControllerV4)
POST /api/v1/language/update (UserLanguageOldController)
GET /api/v1/language/obtain (UserLanguageOldController)
GET /api/v1/language (UserLanguageOldController)
POST /api/v5/auth/users (AuthorizationInfoControllerV5)
PORTUNO
✨ New Endpoints (17)
POST /api/portuno/appconfiguration/v1/create (AppConfigurationController)
POST /api/portuno/appconfiguration/v1/search (AppConfigurationController)
GET /api/portuno/appconfiguration/v1/get/{id} (AppConfigurationController)
GET /api/portuno/appconfiguration/v1/public (AppConfigurationController)
GET /api/portuno/appconfiguration/v1/getAll (AppConfigurationController)
POST /api/portuno/appconfiguration/v1/update/{id} (AppConfigurationController)
POST /api/portuno/appconfiguration/v1/updateBulk (AppConfigurationController)
POST /api/portuno/appconfiguration/v1/delete/{id} (AppConfigurationController)
POST /api/portuno/translations/v1/search (TranslationController)
GET /api/portuno/translations/v1/used-for (TranslationController)
POST /api/portuno/translations/v1/exists (TranslationController)
POST /api/portuno/translations/v1/apply-default-values (TranslationController)
POST /api/portuno/i18n/v1/submit (I18nController)
GET /public/portuno/languages/v1/available (LanguagePublicController)
GET /public/portuno/languages/v1/active (LanguagePublicController)
POST /api/portuno/languages/v1/search (LanguageController)
GET /api/portuno/languages/v1/get/{i18nCode} (LanguageController)
❌ Removed Endpoints (2)
PATCH /api/portuno/languages/{id} (LanguageController)
DELETE /api/portuno/languages/{id} (LanguageController)
⏲️ Deprecated Endpoints (2)
GET /api/v2/appconf (AppConfigurationLegacyController)
PUT /api/portuno/insert/translations (AdminController)
Update in the data:
Hermes
-
The external_sending column is added to the notification table in order to configure which external providers (MAIL, TEAM, etc.) notifications are sent to.
-
Type change in the request_reason column of table workflow_execution
-
New native notification created for incorrect validations on ENRICHED type attributes.
Zeus
-
Permissions granted to roles are renamed based on what is defined in Expand and set application permissions and Changes in existing permissions in Update on the platform
-
Foreign keys have been removed from the user_languaje table to adapt to the changes made to the languages.
-
The previous_login and signed columns have been added to the users table for the additional login information on the home screen and the platform terms of use contract.
Kerno
-
Columns added to the Entity table: the data_access and information_access columns have been added for the new access information feature.
-
Change in attribute_value on the i18n column to adapt to the changes made to the languages.
-
Removal of the MIN_LENGHT and MAX_LENGHT validations on ENRICHED_TEXT_AREA and ENRICHED_TEXT_AREA_INTERNATIONAL
Minerva
-
Extension of the saved_search table to accommodate different filters for both portals, adding search_place and changing sorting_type to be a text string.
Bugs
All the information relating to the problems and limitations that apply to this version or that have been fixed is available in the documentation under Support portal > Known problems and limitations.